HolicSecurity

Passive security audits · By HolicAudit · PDF in 48 hours · Pay in USDT or PayPal

See what anyone on the internet can see about your site.

A passive security exposure audit for a website you own. We check TLS, security headers, cookies, exposed files, software versions against public CVE databases, and your email and DNS records. Within 48 hours you get a plain-English PDF with a prioritized fix list and config you can paste in.

  • Passive checks only, at under 1 request per second
  • Only for sites you own, verified before we start
  • Delivered in 48 hours or a full refund
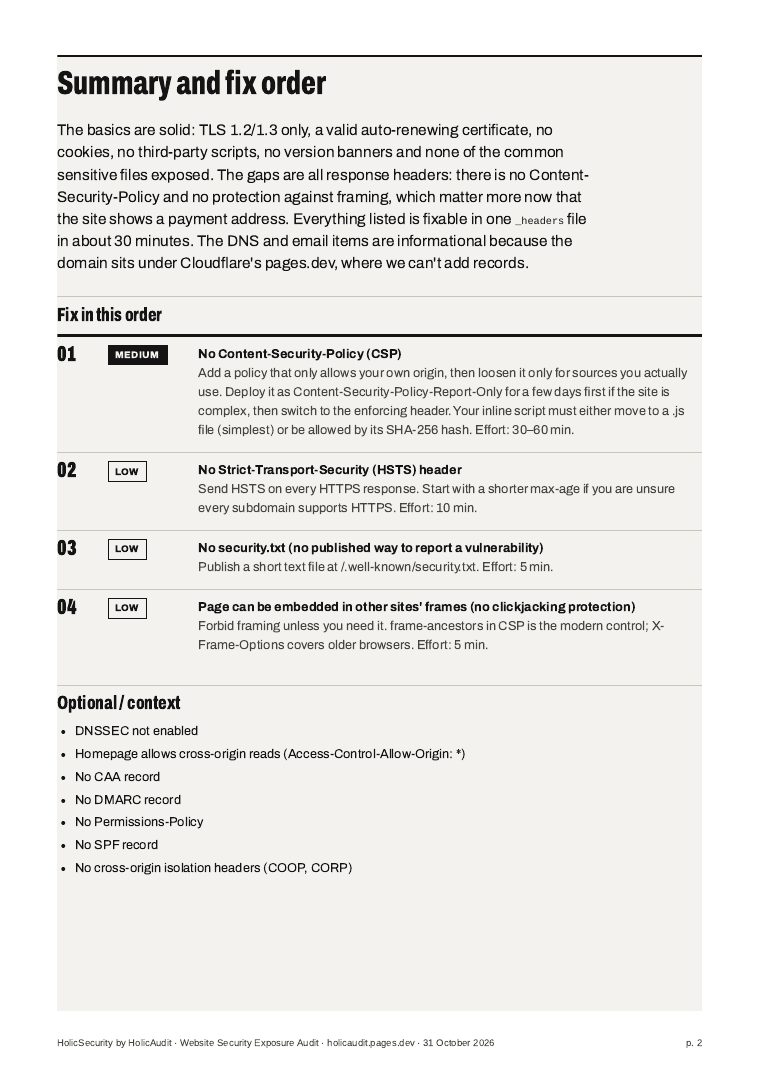
Our own site, audited holicaudit.pages.dev, the real sample report, run on 31 Oct 2026 with 14 HTTP requests and 5 TLS handshakes.
SeverityWhat it meansItems
HIGHFix now: exposed data, or software listed as affected by a known CVE0
MEDIUMFix this month: a missing control that makes a common attack easier1
LOWHardening: cheap to fix, limited impact on its own3
INFOContext or optional, no action needed unless it fits your setup7
PASSChecks that came back clean12

Top item: no Content-Security-Policy header. The report shows the evidence, why it matters, and a ready-made policy for Cloudflare Pages.

We audit only sites whose owners authorise us, so the only public sample we can honestly publish is our own.

What the website security audit checks, and what you get for each item

Every finding has a severity, the raw evidence, why it matters, and the fix for your platform. Each excerpt below is quoted from the sample report. For the full list of checks, read what a passive security audit checks.

TLS and certificate

Which protocol versions your server accepts, whether the certificate chain is valid, and how long until it expires.

TLS 1.0 and 1.1 refused; TLS 1.2 and 1.3 accepted. Certificate valid, 89 days left, auto-renewed by the platform.

Sample report, holicaudit.pages.dev

Security headers

CSP, HSTS, framing protection, nosniff, Referrer-Policy, Permissions-Policy, cross-origin headers and CORS, with a combined config for nginx, Apache, Cloudflare, Netlify or Vercel.

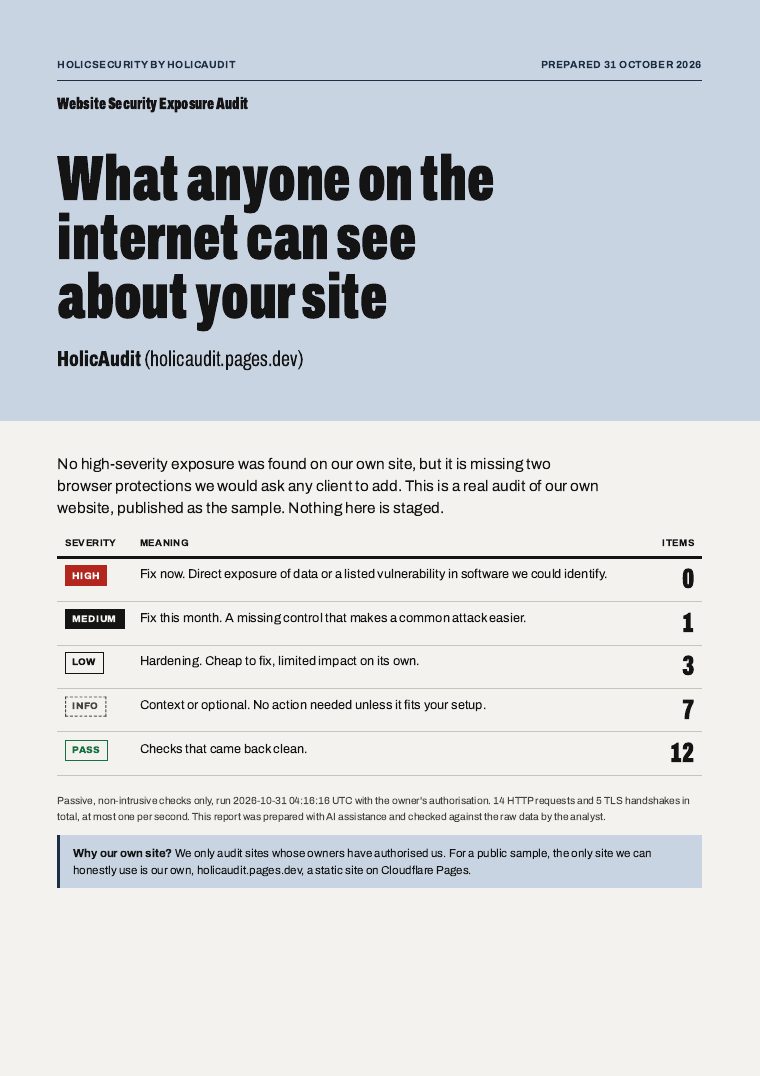
No Content-Security-Policy. The homepage has 1 inline script and 0 external scripts, so a strict policy is practical.

Sample report, holicaudit.pages.dev

Exposed files

A fixed list of well-known files that should never be public, such as /.git/HEAD, /.env and backups. We check existence only and never download contents.

7 common sensitive paths checked, none exposed. We read at most 256 bytes and stored only the yes/no result.

Sample report, holicaudit.pages.dev

Known CVEs in detectable software

Server, CMS and JavaScript library versions your site announces publicly, matched against the NVD and OSV.dev databases.

No versioned libraries or server software detected, so there was nothing to match. When there is, we write "version X is listed as affected by CVE-Y; confirm with the vendor".

Sample report, holicaudit.pages.dev

Email and DNS

SPF, DMARC and common DKIM selectors (can someone send mail as you?), plus CAA and DNSSEC.

No SPF or DMARC record. Reported as Info, because a pages.dev subdomain is not under our control and sends no mail.

Sample report, holicaudit.pages.dev

Honest limits

Every report lists every request we sent, what we didn't test, and why a clean result is not proof of security.

"A passive audit sees what the internet sees. It can't prove a site is secure, and a clean result does not mean there are no vulnerabilities."

Sample report, scope and limits
What the audit found on our own site

holicaudit.pages.dev is a static site on Cloudflare Pages. We audited it with the same tool and rules you'd get, on 31 Oct 2026, and left the findings unchanged.

Findings
SeverityFindingEvidence
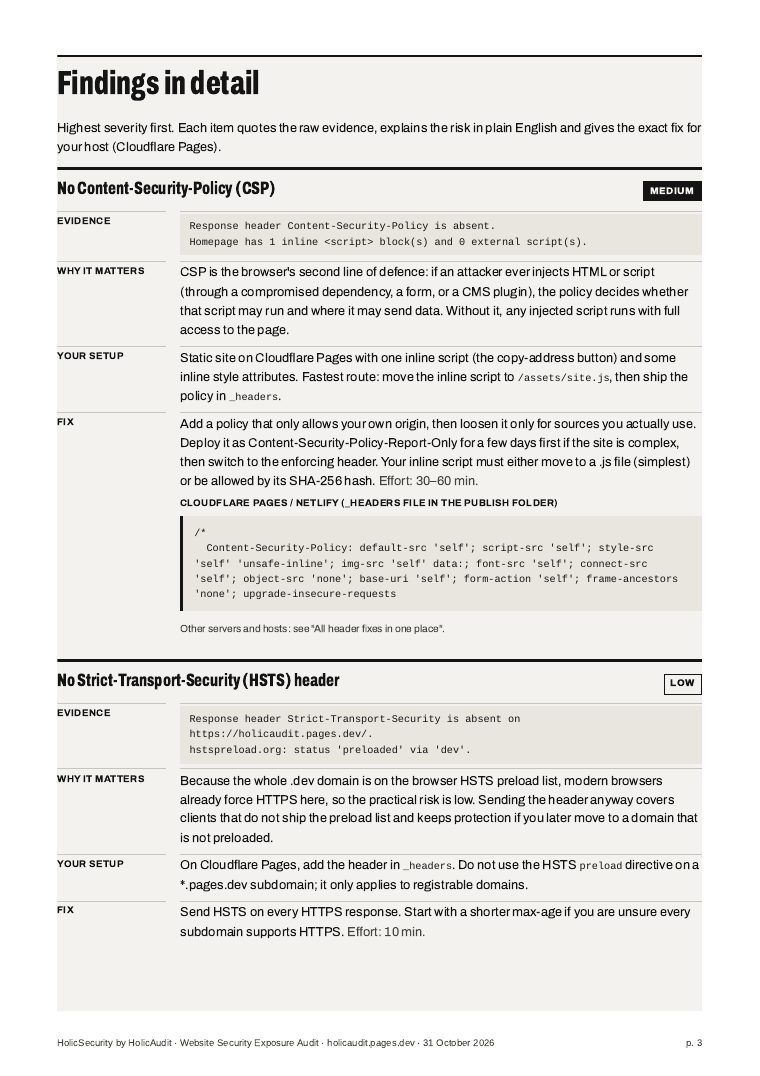
MEDIUMNo Content-Security-PolicyHeader absent. Homepage has 1 inline <script> block and 0 external scripts.
LOWNo Strict-Transport-Security headerHeader absent. hstspreload.org: preloaded via .dev, so browsers already force HTTPS here.
LOWNo clickjacking protectionNeither X-Frame-Options nor CSP frame-ancestors is set.
LOWNo security.txtGET /.well-known/security.txt returned 404.
INFO7 informational itemsNo DNSSEC, CAA, SPF or DMARC (not controllable on pages.dev); no Permissions-Policy; no COOP/CORP; Access-Control-Allow-Origin: * (platform default, no credentials).

12 checks that came back clean

  • Only modern TLS1.0 and 1.1 refused
  • Certificate chain validLet's Encrypt, 89 days left
  • No sensitive files exposed0 of 7 paths
  • No version numbers leakedServer: cloudflare
  • No CVE matchesNo versioned software detected
  • No mixed content3 pages checked
  • No third-party scripts3 pages checked
  • No cookiesSo no cookie flags to fix
  • MIME sniffing offX-Content-Type-Options: nosniff
  • Referrer-Policy setstrict-origin-when-cross-origin
  • No directory listingHomepage is not an index
  • No wildcard CORS with credentialsWildcard is read-only (Info)

One thing we couldn't test: the plain-HTTP to HTTPS redirect, because our network proxy answers plain-HTTP requests itself. The report says so instead of guessing. We haven't applied the fixes to our own site yet; they are written up as a proposal.

Sample security report page 1, cover with severity counts
Page 1 · Cover and severity board
Sample security report page 2, summary and fix order
Page 2 · Summary and fix order
Sample security report page 3, finding detail with evidence and fix snippets
Page 3 · Finding detail with fixes

Open all 15 pages (PDF)

Four steps. Ownership comes first.

We only audit a site after its owner confirms they're authorised and proves control of the domain.

  1. Order and confirm authorisation

    Choose a tier, enter your domain and confirm you own it or are authorised by its owner to order this audit.

  2. Prove you control the domain

    We send you a token. Add it as a DNS TXT record, or as a file on the site. Either one is enough.

  3. Pay in USDT or PayPal

    Pay the exact amount the order page shows, in USDT on the TRC20 (Tron) network or in USD with PayPal.

  4. Get your PDF in 48 hours

    The clock starts once payment and verification are both done. One free revision within 14 days.

Option A: DNS TXT record

Add a TXT record on the domain you want audited. You can delete it after delivery.

example.com.  TXT  "holicaudit-verify=<your token>"

Option B: a file on your site

Publish a plain-text file containing just the token at this path:

https://example.com/.well-known/holicaudit.txt

Security audit pricing. One-off, no subscription.

Pay once per audit. Every tier uses the same passive method and is delivered as a PDF within 48 hours.

Basic

$39 USDT or PayPal

One site, one clear list of what to fix first.

  • 1 hostname: homepage, robots.txt and security.txt
  • TLS, certificate and security-header checks
  • Cookie flags, mixed content and third-party scripts
  • 7 well-known exposed-file checks (existence only)
  • Detectable versions matched against NVD and OSV CVE data
  • SPF, DMARC, DKIM, CAA and DNSSEC lookup
  • Prioritized fix list with snippets for your host
Order Basic

Standard Recommended

$79 USDT or PayPal

Adds the pages that matter most, a ready-made config file and a re-check.

  • Everything in Basic
  • Up to 5 extra pages you choose, such as login, checkout or contact
  • One ready-to-paste header file for your stack: nginx, Apache, Cloudflare, Netlify or Vercel
  • One free re-check within 14 days after you apply the fixes
Order Standard

Plus

$149 USDT or PayPal

For a business with a few hostnames and its own email domain.

  • Everything in Standard
  • Up to 3 hostnames you own (for example www, app, shop), 20 pages in total
  • Hostnames found in public certificate logs, so forgotten subdomains turn up. We list them but don't scan them.
  • Email spoofing review: an SPF, DKIM and DMARC walkthrough for your mail provider
  • Two re-checks and email answers to fix questions for 30 days
Order Plus

Ordering and payment run through the shared HolicAudit order page. Pay in USDT (TRC20) or with PayPal, same price. Turnaround is 48 hours from confirmed payment plus verified ownership. If we can't deliver in 48 hours, you get a full refund. If you can't verify ownership, we refund in full and don't run the audit.

What we will and won't do

This is an exposure audit, not a penetration test. It reads what your site already shows the public, slowly and politely, and stops there.

We will

  • Send a short, fixed list of ordinary requests, at most one per second, identified by our user agent
  • Read public pages, response headers, the TLS handshake and public DNS records
  • Check whether a few well-known sensitive files exist, reading at most 256 bytes to confirm
  • Match software versions your site announces against NVD and OSV.dev
  • Log every request we sent and print the log in your report

We won't

  • Exploit anything, send attack payloads or try to prove a vulnerability by using it
  • Guess passwords, try logins or test authenticated areas
  • Fuzz, brute-force directories or run aggressive scanner modes
  • Load-test or send high request rates
  • Audit any site whose owner hasn't authorised it, including competitors

Satisfaction policy

On time, or your money back

If your report isn't delivered within 48 hours of confirmed payment plus verified ownership, you get a full refund, the same way you paid: USDT back to the address you paid from, or PayPal back to your PayPal account.

One free revision

If something in the report is wrong or unclear, reply within 14 days of delivery and we'll revise it once at no cost.

Free guides

Plain-English explanations of the checks in every report. Fix things yourself, or order an audit when you want the evidence and the config written for you.

Security headers explained

What CSP, HSTS, X-Frame-Options, nosniff, Referrer-Policy and Permissions-Policy do, how to check yours with one command, and a working Cloudflare Pages example.

What a passive security audit checks

Every check we run, the exact sensitive paths we look for, what we never do, and why a clean result is not proof of security.

Honest answers

Is this a penetration test?

No. A penetration test actively tries to break in. This audit only looks at what your site already shows anyone on the internet, and it never attempts an attack. It's a fast, cheap first pass, often the right place to start, but it doesn't replace a professional pentest for a high-risk application.

Will it slow down or break my site?

No. A Basic audit sends about 10 to 30 ordinary HTTPS requests in total, spaced at least a second apart, which is less than one visitor browsing a few pages. Your logs will show our user agent: HolicSecurity-PassiveAudit/1.0.

Why do you need proof that I own the site?

Checking someone else's site without permission can be unwelcome or even illegal, and we won't do it. Adding a DNS TXT record or a small file proves you control the domain. If you're an agency or consultant, the site owner can add it for you.

Can you audit my competitor's site?

No. We only audit sites you own or are authorised to have tested, and ownership must be verified first.

What does "listed as affected by a CVE" mean?

If your site announces a software version, such as a server banner or a JavaScript library file name, we look it up in the public NVD and OSV.dev databases. A match means that version is listed as affected. It doesn't prove your site can be exploited, because patches may be backported or the vulnerable feature may be unused. Confirm with the vendor's advisory. We never test whether it can be exploited.

Does a clean report mean my site is secure?

No. It means nothing in our passive checks turned up a problem. Hidden software versions, application logic, authenticated areas and server internals are outside what a passive audit can see. The report lists these limits.

How do I pay?

Two ways, same price, both through the order page, which gives you an order number and the exact amount.

USDT on the TRC20 (Tron) network only. Funds sent on another network or as another token can't be recovered.

PayPal in USD to paypal.me/maicoden, with your order number in the note. PayPal payments are confirmed by hand, usually within a few hours.

The 48-hour clock starts once your payment is confirmed and you've verified that you own the site.

How are reports made?

Data collection is automated and every request is logged. Findings come from fixed rules, the explanations are written with AI assistance, and each finding is checked against the raw evidence printed in the report.

What happens to my information?

We collect only what the audit needs. Scan data and your intake details are deleted 90 days after delivery, and we never sell or share them. A USDT transaction is permanently public on the Tron blockchain; PayPal payments are processed by PayPal under its own privacy policy. See the Privacy policy.

Who runs this?

HolicSecurity is the security line of HolicAudit, which also makes SEO and competitor audits. Same team, same order page, same refund policy.

Questions before you order?

Email us at holicaudit@mail.grokbot.com